1. I Performed Forensics on a Server and It Got Somebody Fired

    Wed 04 November 2026

    This is a 'fun' little story from 'a long time ago' when I worked in IT security.

    Introduction

    The other day I got an unexpected call from a customer. They had taken a Windows server offline because it was performing a DoS attack on a Russian webshop at line-rate (1Gbit) speed and the traffic pushed away legitimate traffic to critical customer facing applications.

    That was quite an incident for them and they wanted to know what happened to this server. How did it get compromised?

    Over confidence

    Our company was not specialised in digital forensics and I had only brief experience with it, mostly out of curiosity. I was upfront about this to the customer, but I told them that I was confident I could figure out what happened and we accepted the job.

    The customer had taken the affected machine offline and either created a disk image or shared the virtual machine disk image with us. They shipped the server image on a portable hard drive to us, probably through a courier, because it was all on short notice.

    Scrambling for a forensic system

    Meanwhile, I took an old HP Compaq DL380 G2 server we had lying around and stuffed it full of SCSI disks to create a RAID array on which to store the image. I'm not sure exactly why I chose to do this. Probably because we needed the storage capacity, but also because I remember that performing the analysis put a lot of stress on the storage and creating a RAID array would speed things up. I might have setup a RAID 0 just for the capacity and performance, in lieu of redundancy, which wasn't important.

    We had a one gigabit network connection to the DL380 I turned into an ad-hoc forensic server and I remember that transferring the disk image onto the server took ages.

    Looking for evidence

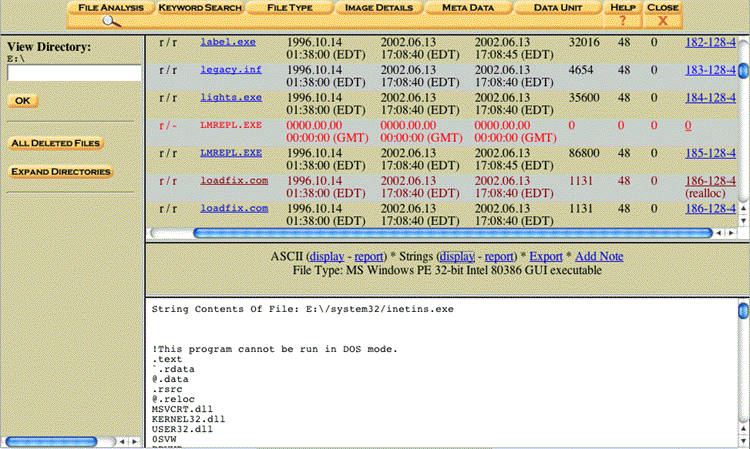
    I used the The Sleuth Kit Autopsy Forensic Browser to find my way through the disk image. You may ask: to find what exactly, what are you looking for?

    It's quite simple: I wanted to know what files has been created, modified or deleted on disk during the time the customer suspected the system was compromised.

    As I dug deeper into the image, I was able to find several created and deleted files that showed exactly what happened and why the system was compromised. Even if you delete a file, it's not really deleted from disk. The data and meta-data is still there, only the meta-data of the file is modified to mark it as deleted.

    It turned out that somebody with access to the server had installed a 'keygen' or 'crack' for a particular software product (I can't recall which software they cracked)1. Unfortunately that keygen (or crack) was infected with malware and that was how the system got compromised. This behaviour is somehting I would not expect an external attacker, I mean: why would they do this? It looked more like the unwise actions of a sysadmin.

    That realisation made me feel stunned for a moment: that somebody would use a crack or keygen at their job. Crazy.

    Who dun it?

    Now we knew what happened, we still didn't know who did this. Still in disbelief, I copied the disk image to a computer and used a VMware product to boot the compromised disk image inside of a virtual machine (without network connectivity).

    We used regular tools to reset the administrator password of the image so we could log in and look at the system logs of the windows server. There we could find with little effort which user downloaded and ran the infected executable.

    The aftermath

    Days later, after I finished my report and shared my findings with the customer, everything went silent. At some point I contacted the customer just to check-in, only to learn that the customer's employee - my person of contact who asked me to perform this forensic research - was no longer working with the company...


    1. A keygen or key generator is a small piece of software that generates valid licence keys for software. A crack is a small piece of software that patches the software so that it does not require a licence key. ↩
    If you have any comments email me, see the About page for contact details.
  2. Don't Be a Tech Bro

    Mon 26 October 2026

    David Heinemeier Hansson (DHH) created a blog post (October 2026), encouraging men to embrace their 'tech bro' identity.

    David, you write:

    We should all strive to be our brother’s keeper: to look after each other,
    inspire each other, and simply enjoy each other’s company. For men this
    usually requires a shared mission or interest. Mine has always been
    computers, so I happily consider myself a tech bro.
    

    The message is clear: you consider tech a topic for men to shared between men and the choice of words is clearly and deliberately exclusionary to women.

    I know the term has been used to denigrate anyone who has done
    well with computers or who dares to be excited about them in ways
    that rub some people the wrong way. But who cares? There is no reason
    to surrender a perfectly pleasant term of endearment just because
    small-minded people deploy it to discredit opinions they dislike.
    

    David, being exited about technology - maybe even in a socially awkward way - makes you a nerd and that's actually a real term of endearment.

    Their interest in computers, or their skill with them, is not the problem. 
    

    True, but we never said it was a problem. You know full well why 'tech bro' is a pejorative. Because the 'bro' part is the problem. It's about the gendered part.

    Neither is their gender. Yes, men dominate computing. There are many reasons
    for that; none of them justifies collective guilt. The fact that women are a
    minority does not diminish the many who work in the industry, and it is more
    than fine to celebrate their achievements with gusto. Turning the percentages
    into a struggle session is nonsense.
    

    Look at how fast you pass over the 'many reasons' why women are a minority in tech. Because you know full well a huge reason is gatekeeping in the form of sexism.

    The 'struggle session' you dismiss is actually the point. It shows it's not a merit-based environment as you claim it to be. Whatever you may think of as the 'achievements' you talk about, these achievements are tarnished1, in part because of discrimination against women.

    I think that's the criticism that triggerd you to write your blog post. It's so typical to double down when faced with criticism. It's not a merit, unfortunately, it's more a possible sign of emotional disregulation.

    So if you are a tech bro committed to advancing technology, celebrating
    progress, and rejecting managed decline, you are indeed my brother. I will
    always want to shake your hand and cheer you on.
    

    You are not subtle David. You consider allowing more women in tech as 'managed decline'. We understand your point. What I don't understand is: why make it in the first place?

    David, are you OK?

    David, you are a multi-millionaire. You won the game of capitalism, you don't have to prove anything to anyone anymore. You built Ruby on Rails. You should be secure in your identity.

    So why do you need to embrace the tarnished 'tech bro' identity? Why do you need to be validated in your masculinity, and dismiss women? And why do you need to dismiss minorities so much? Why are you so focused on identity politics?

    First the racism, now the sexism. Ideas not supported by science. Ideas not based in any merit.

    Frankly speaking, I think that people who express racism and sexism, are not secure in their own identity, and only feel secure if they diminish and discard the identity of others. David, please consider exploring your unhappiness/frustration with a professional, in private. Don't espress it in a blog post.

    At this point, I think you are a liability for 37signals and their customers, the Ruby (on rails) community and tech at large. Your blog post is yet another piece of evidence people critical of 'tech bros' and 'tech bro' culture can point at, to convice others. You are making it really easy, saying the quiet part out loud.


    1. and the sexism is only one part of the overall criticism of the whole tech industry and the negative impact on our society as caused by tech bros. ↩

    If you have any comments email me, see the About page for contact details.

Page 1 / 117